PinkCore的新游戏
安装包
https://stat-r.nwmtfw.com/gsf/closedBeta/0923_0_Cursed_Blossom_Festival_of_Euphoria_CBT.apk
资源下载流程在登录账号前
部分资源包被加密加密文件魔数 EBX1
解密相关函数在
ProjectInfinity::EncryptedAddressable::XorBundleCipher
但是没找到
struct XorBundleCipherConfig {
    struct XorBundleCipherConfig__Class *klass;
    MonitorData *monitor;
    struct String *keyString;
};
keyString是怎么赋值的
也就缺少了解锁密钥
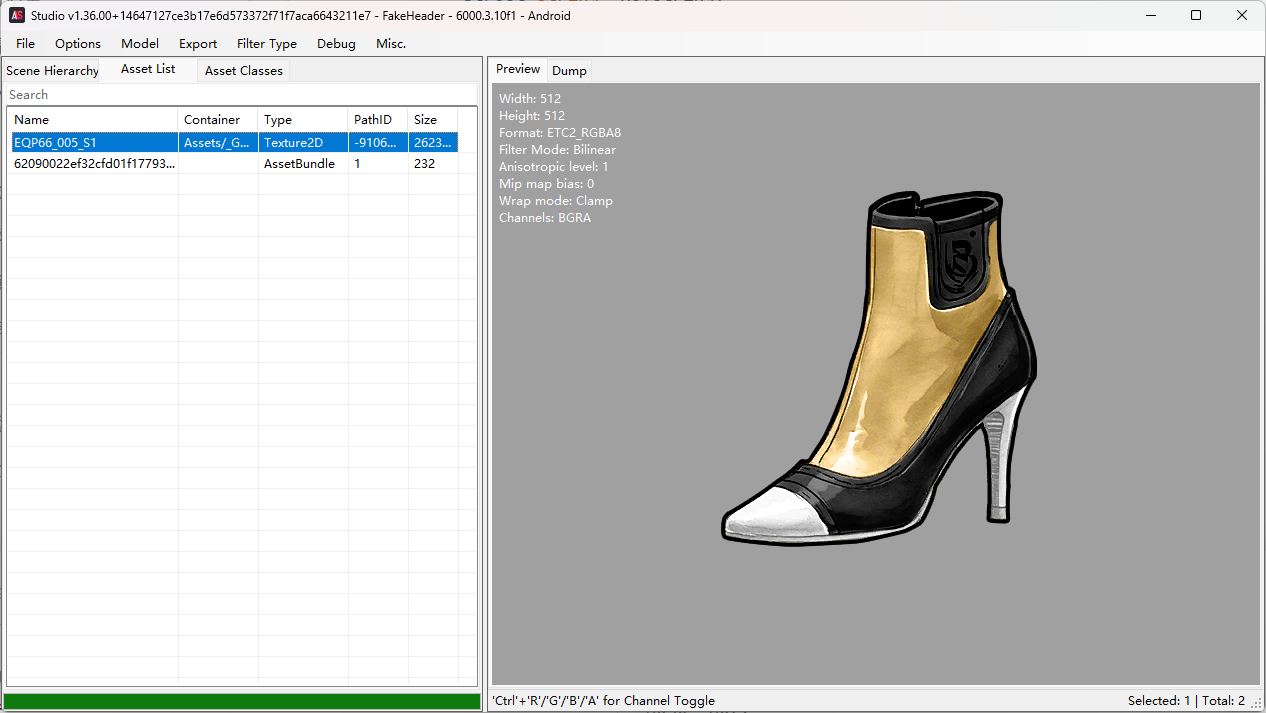
加密文件样本
https://ig-download.pinkcore.net/AssetBundle/prod/Android_Erolab/catalog_2026.09.23.07.00.45/itembigicon_assets_itembigicon_eqp66_005_s1.bundle
36bytes明文对照硬推,样本测试是可以的
00-03:魔数
05-08:数据大小
0D- :ab开始
测试脚本
#!/usr/bin/env python3
# -*- coding: utf-8 -*-

def decrypt_unityfs(input_file, output_file, start_offset=0x0D):
    """
    从文件的 start_offset (0x0D) 开始,使用 22 字节密钥进行异或解密
    """
    # 22 字节循环密钥 (从你提供的明文/密文推导)
    key = bytes([
        0x45, 0x44, 0x46, 0x4A, 0x3E, 0x3C, 0x4D, 0x45, 0x23, 0x28, 0x43,
        0x28, 0x29, 0x56, 0x2A, 0x23, 0x3C, 0x4D, 0x3C, 0x3E, 0x44, 0x66
    ])
    key_len = len(key)

    # 读取整个文件到内存 (如果是超大文件可改为分块读写)
    with open(input_file, 'rb') as f:
        data = bytearray(f.read())

    print(f"[*] 文件大小: {len(data)} 字节")
    print(f"[*] 将从偏移量 0x{start_offset:X} 开始解密...")

    # 从 start_offset 开始,密钥从索引 0 开始循环使用
    for i in range(start_offset, len(data)):
        key_index = (i - start_offset) % key_len
        data[i] ^= key[key_index]

    # 写入解密后的文件
    with open(output_file, 'wb') as f:
        f.write(data)

    print(f"[+] 解密完成!输出文件: {output_file}")

    # 打印解密后开头几个字节确认(应该是 UnityFS)
    header = data[:0x10]
    try:
        print(f"[*] 文件头前16字节 (hex): {header.hex(' ')}")
        print(f"[*] 文件头 ASCII 预览: {header.decode('ascii', errors='replace')}")
    except Exception:
        pass

if __name__ == "__main__":
    # ========== 直接修改下面两个路径即可使用 ==========
    INPUT_FILE  = "itembigicon_assets_itembigicon_eqp66_005_s1.bundle"   # 待解密的输入文件
    OUTPUT_FILE = "decrypted.dat"   # 解密后的输出文件
    # ================================================

    import os
    if not os.path.exists(INPUT_FILE):
        print(f"[-] 找不到输入文件: {INPUT_FILE}")
        print("请修改脚本内的 INPUT_FILE 变量,或通过命令行参数传入。")
    else:
        decrypt_unityfs(INPUT_FILE, OUTPUT_FILE)
1 个赞